Grants Fix
24 hours
$149
- Diagnose "permission denied" (42501) errors
- Least-privilege grant migration
- RLS stays on
- One retest
Departures · AI-built apps · Supabase + Stripe
Built your app with an AI tool, and people are about to sign up and pay? In 48 hours we fix what usually breaks at launch (a security audit that fixes, not just lists), then prove it: one customer can't see another customer's data, and nobody gets your paid plan for free.
Fixed price from $149 · founding price $399 for the first five Launch Passes
Two or more yes? This was made for you.
Not sure what your app runs on? If Lovable or Bolt set up your logins and database, it's almost certainly Supabase. Send us your app link and we'll tell you for free.
Not a fit yet: apps on Firebase or a custom backend, and projects with no users or payments. Send us a request anyway and we'll point you in the right direction.
A launch-readiness pass is a fixed-price review and repair of the problems that most often break AI-built apps on launch day: user data leaking between accounts, paid features unlocked for free, and auth or email that fails in production. GoodToLaunch fixes them in one pull request, then proves each fix on your own app.
AI coding tools are very good at getting an app to work. They are less careful about who can read which rows. In May 2025, security researchers checked 1,645 apps built with Lovable and found 170 that let anyone read personal data, because row level security was missing. The issue was recorded as CVE-2025-48757; Lovable disputes it, saying each app owner is responsible for their own data. Scanners can tell you a problem might exist. A pass fixes it and shows you it's gone.
What goes wrong: row level security is off, or a policy says using (true), so any signed-in user (or anyone with your public key) can read everyone's rows.
How we prove it: two test accounts. User B tries to read, insert, update and delete user A's rows. Every attempt must fail, and the results table goes in your report.
What goes wrong: a grants change leaves you with 42501 permission denied for table, and the quick fix your AI suggests is to disable RLS or grant everything to anon.
How we prove it: a least-privilege grant migration that keeps RLS on, followed by the same two-account test.
What goes wrong: a retried, duplicated or out-of-order checkout.session.completed grants Pro twice, or an unsigned event grants it for free.
How we prove it: we replay duplicate, concurrent, out-of-order and forged events in Stripe test mode. Each payment must change access exactly once.
What goes wrong: magic links point at localhost, OAuth redirects fail on your real domain, or Supabase's default email limits stop signups on launch day.
How we prove it: a fresh signup, login and password reset on the production domain, recorded step by step.
What goes wrong: an unauthenticated route calls your model provider, and one script runs up the bill overnight.
How we prove it: auth on every AI route, rate limits and a hard spend cap, each tested from a signed-out session.
Send us your app URL, stack and launch date through the request form. You sign a one-page engagement letter and a testing authorization, then share a staging copy, test accounts and Stripe test mode. No database password, no production secrets.
We find the launch blockers and fix them in one pull request on your repo, with tests. You or your developer review and merge it.
We rerun every check on the fixed branch: two-account isolation tests, Stripe event replays, and a fresh signup on your real domain.
You get a plain-language proof report within 48 hours. Your data is deleted within 14 days. Add a monthly retest if you ship often.
24 hours
$149
Now boarding · 5 founding seats
48 hours
$499 $399 founding price for the first 5 customers
24–48 hours, priority
$1,200
Retest, $149/month. We rerun your proofs after deploys, up to twice a month, and send a short report of what changed. Renews monthly until you cancel; cancel any time by email.
Work outside the listed scope is quoted before we start, at $110/hour. A pass covers the listed checks as of its date. It is not a guarantee that an app can never be breached.
Store-Ready is a pre-submission check for AI-built mobile apps. We go through the things reviewers reject for, fix what we can, and hand you an evidence pack before you press Submit.
What goes wrong: the app looks thin or templated (Apple guidelines 4.2 and 4.3), the demo login fails, a screen still shows placeholder text, or a link goes nowhere (2.1).
What you get: a walkthrough as a reviewer would do it, with a fix list in priority order.
What goes wrong: an app that lets people sign up must let them delete the account from inside the app (5.1.1(v)). AI tools often skip it.
What you get: proof that deleting an account really removes the data, recorded step by step.
What goes wrong: a third-party SDK ships without its own privacy manifest and the upload is blocked (Apple error ITMS-91061).
What you get: your build and lockfile checked against each SDK's manifest requirements.
What goes wrong: Apple's privacy label and Google's Data Safety form say different things from what the app actually collects.
What you get: both forms checked against the real traffic and SDKs, with the corrected answers.
What goes wrong: a new store requirement lands and your next release is blocked.
What you get: the upcoming deadlines that affect your app, in the report.
per release, done by hand
$149 per release
Already rejected? Paste the rejection message in your email and we'll tell you which of these it maps to.
Not a guarantee. Apple and Google make the final decision. Store-Ready lowers the chance of a known, avoidable rejection; it doesn't promise approval.
| Feature | Security scanner | Marketplace fixer | Agency audit | GoodToLaunch |
|---|---|---|---|---|
| How it is priced | Usually a subscription | Per gig, varies by seller | Usually quoted per project | $149–1,200 fixed |
| Fixes the problem | No, lists findings | Usually | Sometimes | Yes, as a pull request |
| Proves the fix on your app | No | Rarely | Varies | Two-account tests + Stripe replays |
| Stripe webhook testing | No | Rarely | Varies | Yes |
| Who does it | Automated | Varies | A team | OSCP + CISSP certified team, 10+ years in security and backend engineering |
| Turnaround | Minutes | Varies | Varies | 24–48 hours |
General categories, not named vendors. Individual products and sellers differ, so check what any provider actually tests and delivers before you buy.
Sample proof report · fictional app
Parcelry GOOD TO LAUNCH
The sample is a fictional app, shown so you can see the format before you buy.
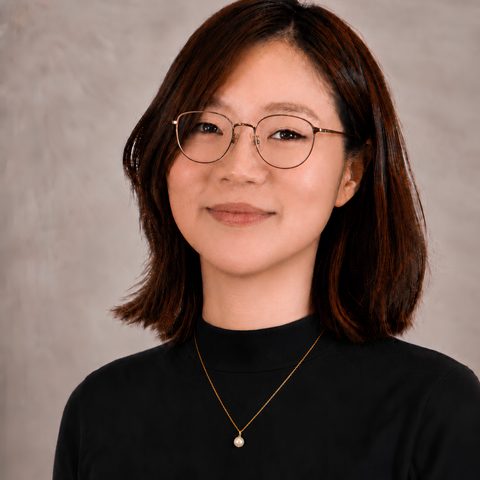
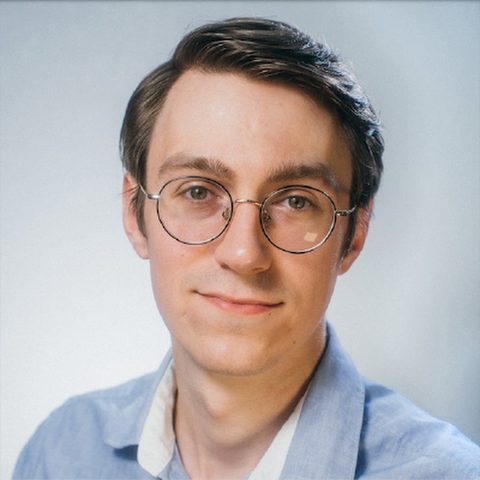
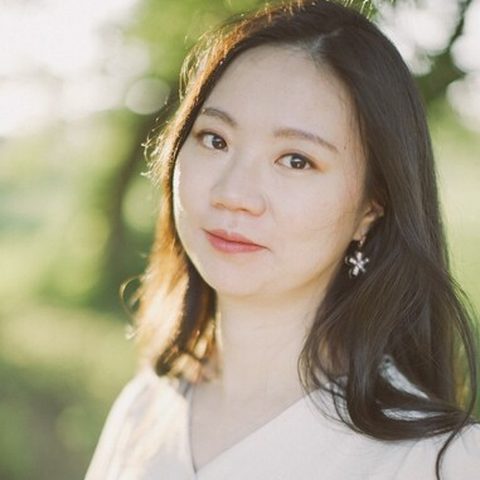
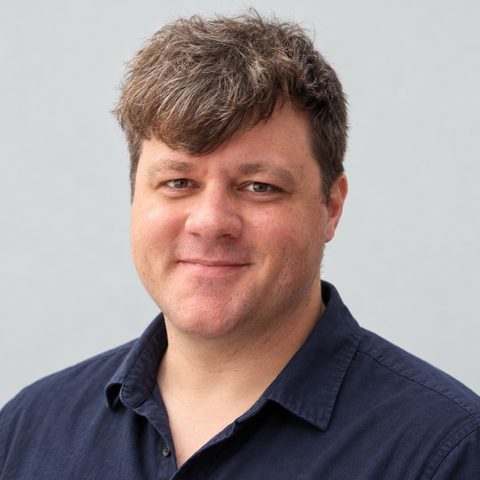
Four people, one job each. Jordan is your first contact: questions, scheduling and keeping your pass on time. He leads sales and marketing. Sumin runs the first pass: intake, the testing authorization and the initial web checks on who can see what. Matthew builds and ships production web apps, and works on the fix side: clean pull requests and deployment settings. Su leads every pass and proves the fixes: the two-account tests, the Stripe replays and the report.
You deal with us directly, from the first email to the report.
Every engagement starts with a signed testing authorization. We only test what you own, on staging, with test accounts.
using (true) policies, and prove user B cannot read user A.No. We work on a staging copy with test accounts and Stripe test mode, under a signed testing authorization. You review and merge the pull request yourself.
For data isolation, we sign in as two different test users and show that user B cannot read, write, update or delete user A's rows. For Stripe, we replay duplicate, out-of-order, concurrent and unsigned webhook events and show that each payment grants access exactly once.
No. It's a tested scope as of a date: the checks listed above, proven on your app at the time of the pass.
You can, and for many problems you should. The risk is that the suggested fix for a permissions error is often to disable row level security or grant everything to anonymous users. The error goes away because the data is exposed. A pass fixes it and then tests it from a second account.
Apps on Supabase (database and auth) and Stripe (payments), built with Lovable, Bolt, Cursor, Claude Code, v0 or by hand. Other stacks aren't supported yet.
24 hours for a Grants Fix and 48 hours for a Launch Pass, counted from signed authorization and staging access.
No. Live apps with real users are where a leak costs the most. We still work on a staging copy, then you deploy the merged fix.
Yes, with Store-Ready ($149 per release). We walk through the app as a reviewer would, check account deletion, privacy manifests and SDKs, and compare Apple's privacy label with Google's Data Safety form. It lowers the chance of a known, avoidable rejection, but Apple and Google make the final decision.
A team of OSCP- and CISSP-certified security engineers with 10+ years in security and backend engineering. Su, a launch security engineer, leads every pass and does the testing and proof. Sumin, a web application security engineer, runs the first-pass checks. Matthew, a cloud security engineer, works on the fixes.
Gate B · Now boarding
Send your app URL, your stack and your launch date. We reply within one business day with what we'd check and when we can start.
Request a passPrefer email? Copy the address: hello@goodtolaunch.com